 info@cultbooking.com
 0049 30 726225 0

Credit Card Security and PCI DSS Compliance
Protecting payment-card data is a core part of the security architecture of Cultuzz Digital Media GmbH and its CultBooking service.




How the Process Works
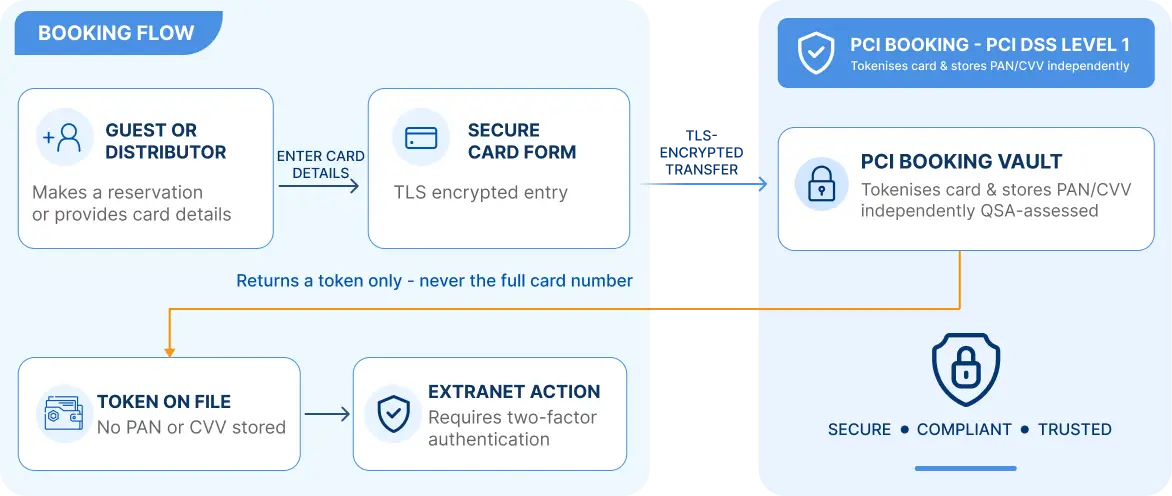
Five steps take a guest’s card details from entry to a permitted, tokenised booking action - without the full card number ever coming to rest inside CultBooking, CultSwitch or MappingMaster.
Secure Receipt of Cardholder Data
Depending on the booking source, cardholder data is either entered by the guest through CultBooking’s secure payment-card form or received from an authorised distributor.
Secure transfer to PCI Booking
In both cases, the cardholder data is securely transferred to the PCI Booking environment through an encrypted connection. CultBooking is designed to pass the data to PCI Booking for secure handling and do not retain the full card number or card security code.
Tokenisation instead of card-data storage
PCI Booking securely stores the cardholder data in its protected payment-card vault and provides a unique token. CultBooking uses this token to reference the stored card for permitted booking and payment-related processes.

This architecture significantly reduces the amount of sensitive cardholder data handled by CultBooking, CultSwitch and MappingMaster.
PCI DSS responsibilities nevertheless depend on the complete assessed environment — including the relevant integrations, infrastructure, access controls and operating procedures.
PCI BOOKING’S PCI DSS STATUS
PCI Booking Ltd. is our payment-card vault and tokenisation provider. PCI DSS Level 1 Service Provider is the formal industry designation used by PCI Booking for its PCI DSS status.
PCI Booking provides tokenisation and secure payment-card storage services, replacing sensitive card data with unique tokens for use in integrated payment processes.
PCI Booking’s cardholder-data environment is independently assessed by a Qualified Security Assessor (QSA).
Cultuzz Digital Media GmbH
PCI DSS status
Cultuzz Digital Media GmbH has completed the following PCI DSS compliance documentation for the CultBooking and CultSwitch services:
- Self-Assessment Questionnaire D (SAQ D) for Service Providers.
- Attestation of Compliance (AoC).

Self-Assessment Questionnaire D for Service Providers and Attestation of Compliance For use with PCI DSS Version 4.0.1 Revision 2
Publication Date: January 2025
The assessment was completed on 1 June 2026 in accordance with PCI DSS v4.0.1 Revision 2.
The date refers to the completion date of the assessment. The SAQ and AoC apply to the assessed Cultuzz Digital Media GmbH environment and the services covered by the relevant compliance documentation.

We review our PCI DSS compliance at least annually and maintain the applicable technical and organisational measures required to protect payment-card data throughout the booking and payment process.
Subject to applicable confidentiality arrangements, we can provide Cultuzz Digital Media GmbH’s current SAQ D and AoC on request.
Request our compliance documentation
Contact us to request any of the following, subject to applicable confidentiality arrangements: